Critical OpenSSH Vulnerability Exposes Linux Servers to Passwordless Attacks
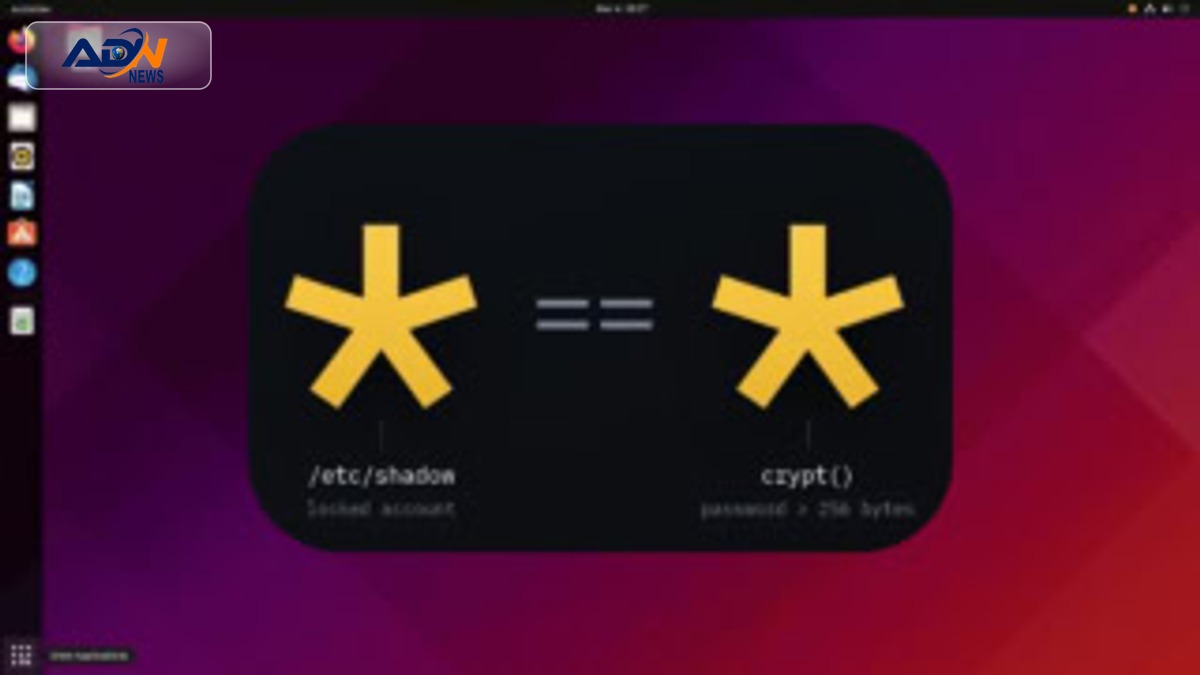
KARACHI: A severe vulnerability in OpenSSH has been identified, allowing attackers to access certain Linux servers without the need for a password. This flaw, humorously dubbed the “*sshole” vulnerability by its discoverer, security researcher Özgün Kültekin, was disclosed on November 5 and primarily affects Alpine Linux and other systems utilizing the musl C library.
In response to this critical security threat, OpenSSH developers promptly released an emergency patch on the same day of the disclosure. Kültekin’s findings highlight a significant risk for users of affected systems, emphasizing the urgent need for updates to safeguard against potential breaches.
The implications of this vulnerability are far-reaching, as it poses a serious threat to the integrity of Linux servers widely used in various sectors, including finance, healthcare, and government. Cybersecurity experts warn that without immediate action, organizations could face unauthorized access, data breaches, and significant operational disruptions.
As the cybersecurity community rallies to address this issue, users of affected systems are urged to apply the emergency patch without delay. Ongoing monitoring and further investigations into the vulnerability’s impact are expected in the coming days, as experts work to ensure the security of Linux environments globally.